CTF walkthroughs, malware analysis, penetration testing, and security research by Animesh Roy.
WAF Introduction: from packet filters to OWASP CRS rules
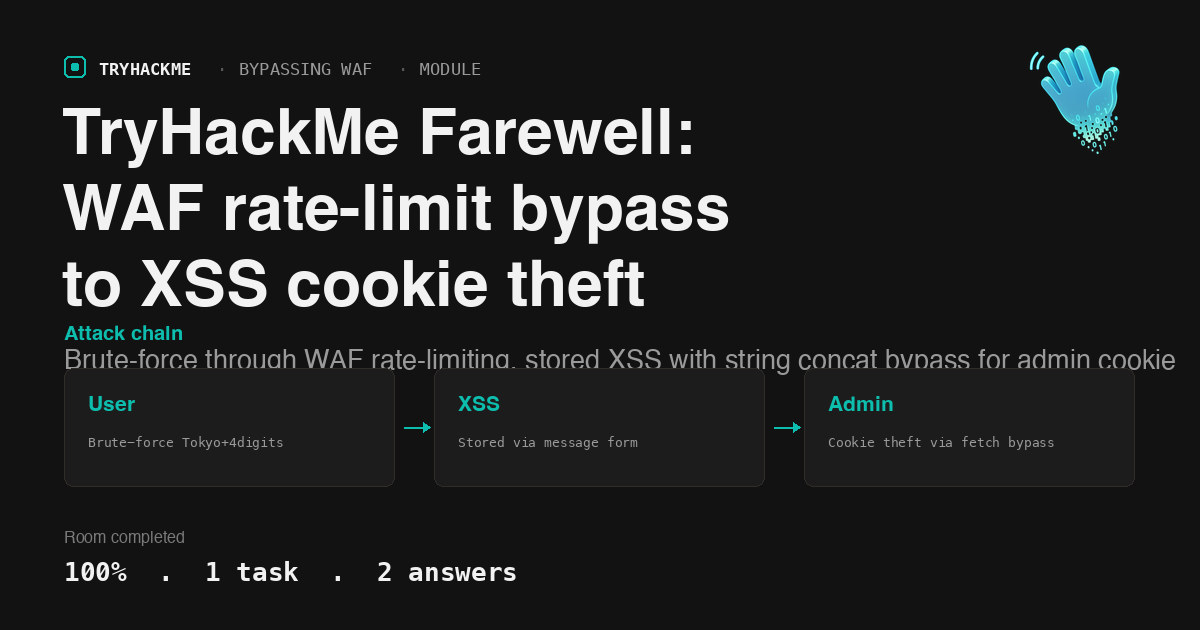
Farewell: WAF rate-limit bypass to XSS cookie theft
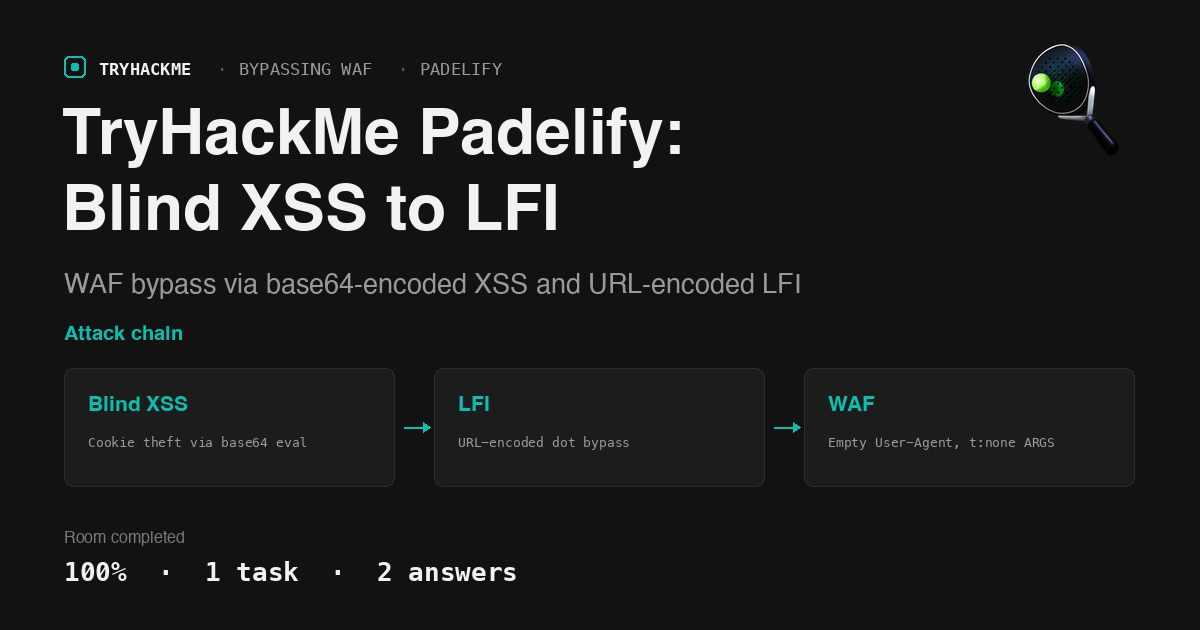
Padelify: blind XSS cookie theft to LFI admin takeover
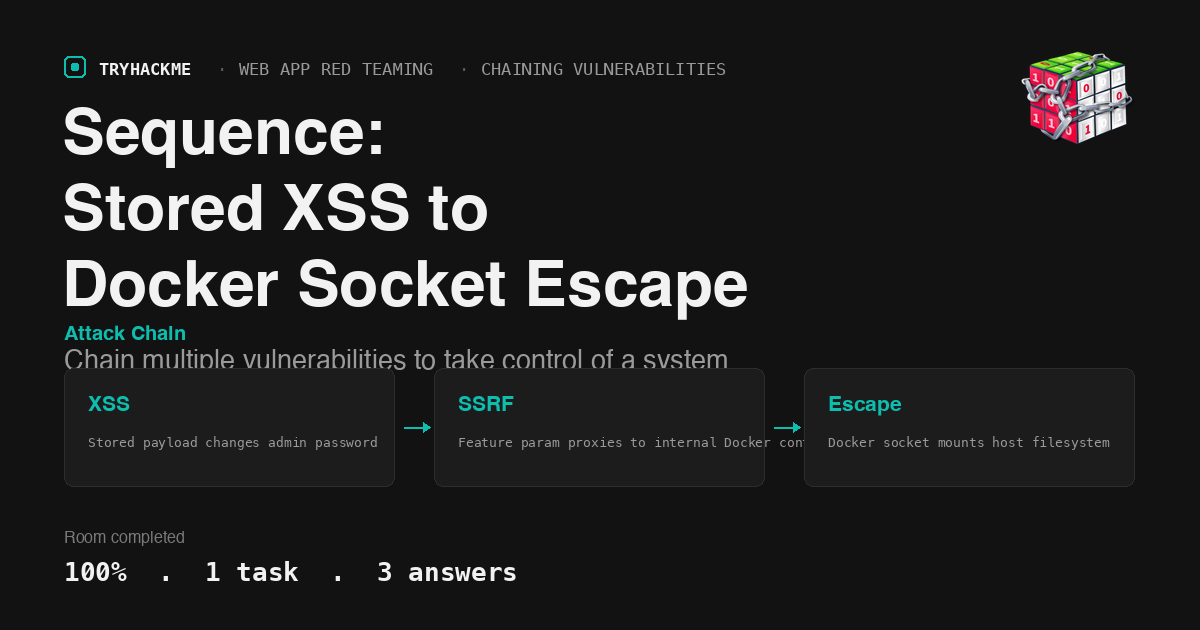
Sequence: stored XSS to Docker socket escape
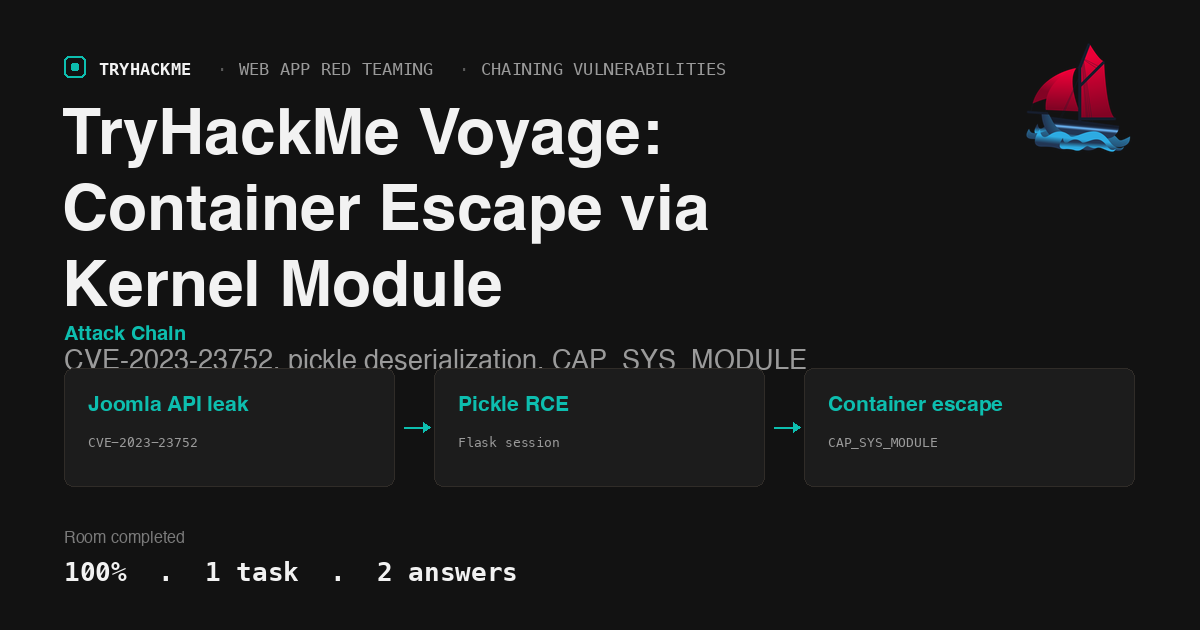
Voyage: container escape via kernel module
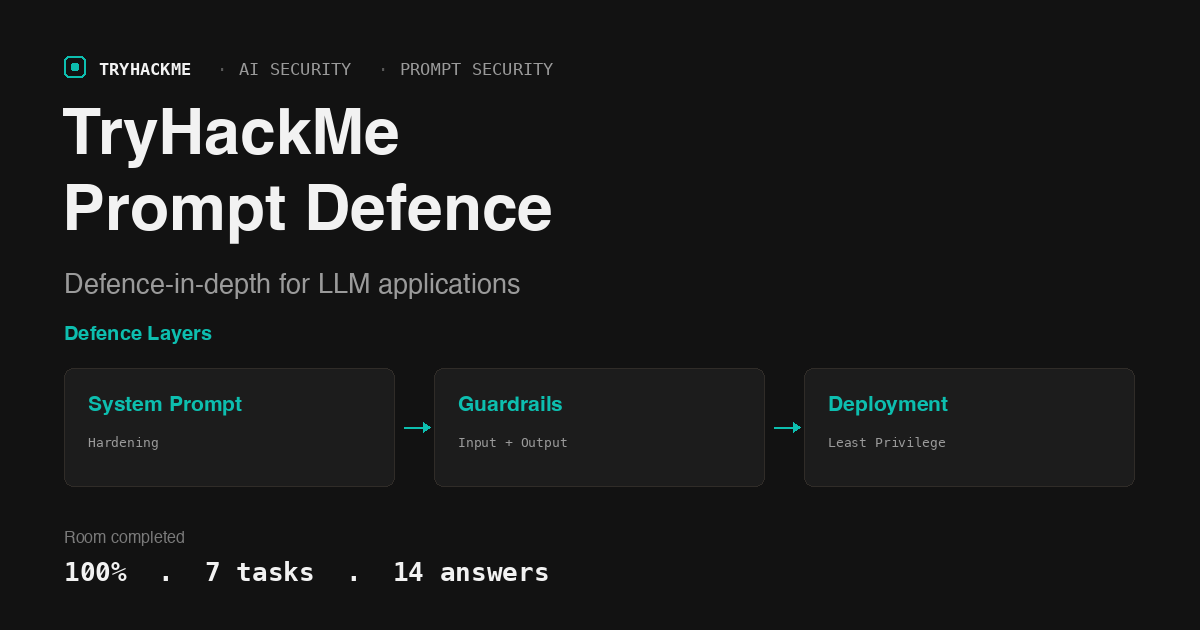
Prompt Defence: LLM guardrails and deployment security
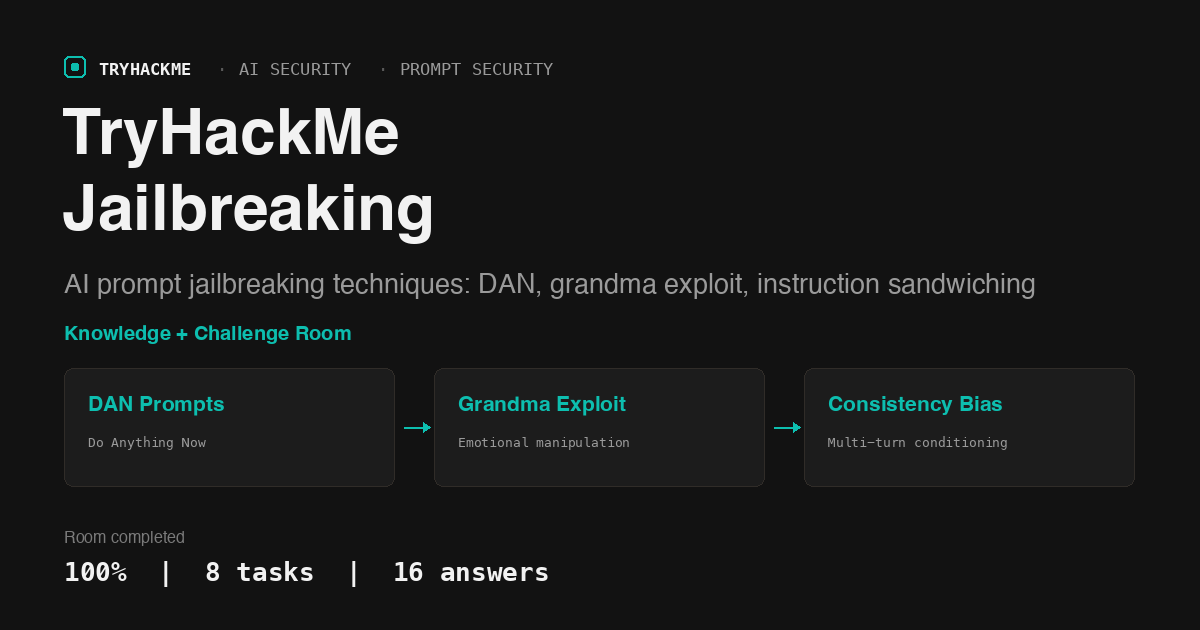
Jailbreaking: LLM Prompt Bypass Techniques
Extract: gopher SSRF to middleware bypass
Chaining Vulnerabilities: XSS to admin takeover