Classroom
Posts
Categories
Tags
Archives
Search
About
Home
Categories
TryHackMe
HTTP request smuggling
HTTP Request Smuggling: CL.TE desync exploitation
CORS
CORS and SOP: cross-origin data exfiltration
DOM-based XSS
DOM-Based Attacks: stored XSS via Vue v-html exploitation
CSRF
CSRF: token bypass and SameSite cookie exploitation
cross-site scripting
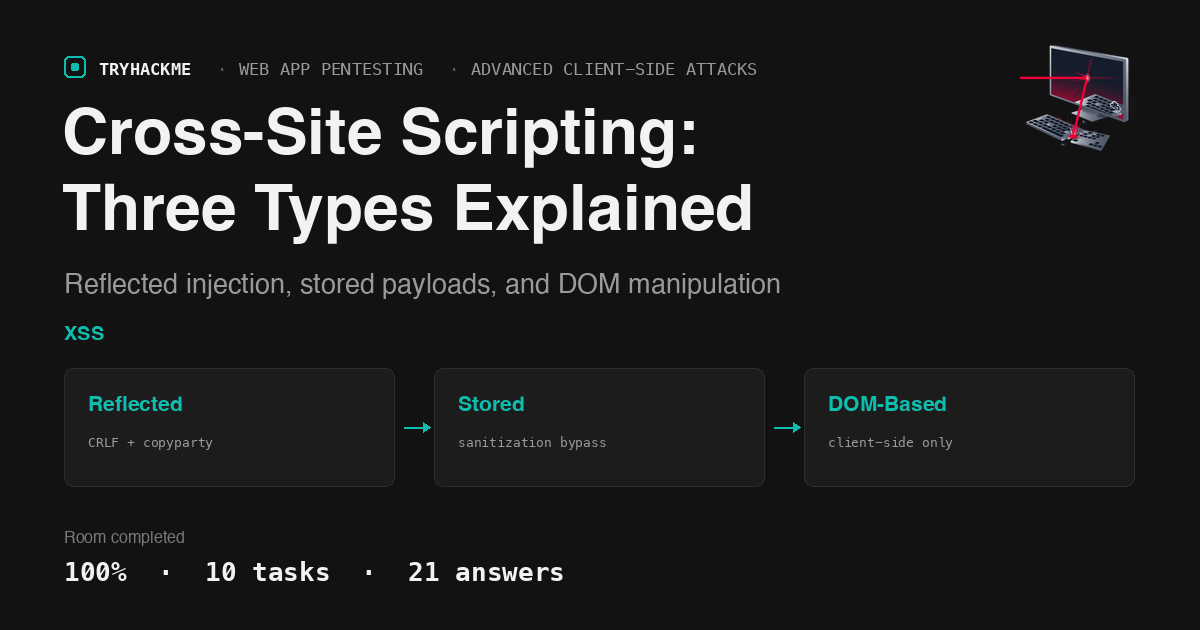
XSS: reflected, stored, and DOM-based scripting attacks
SSRF
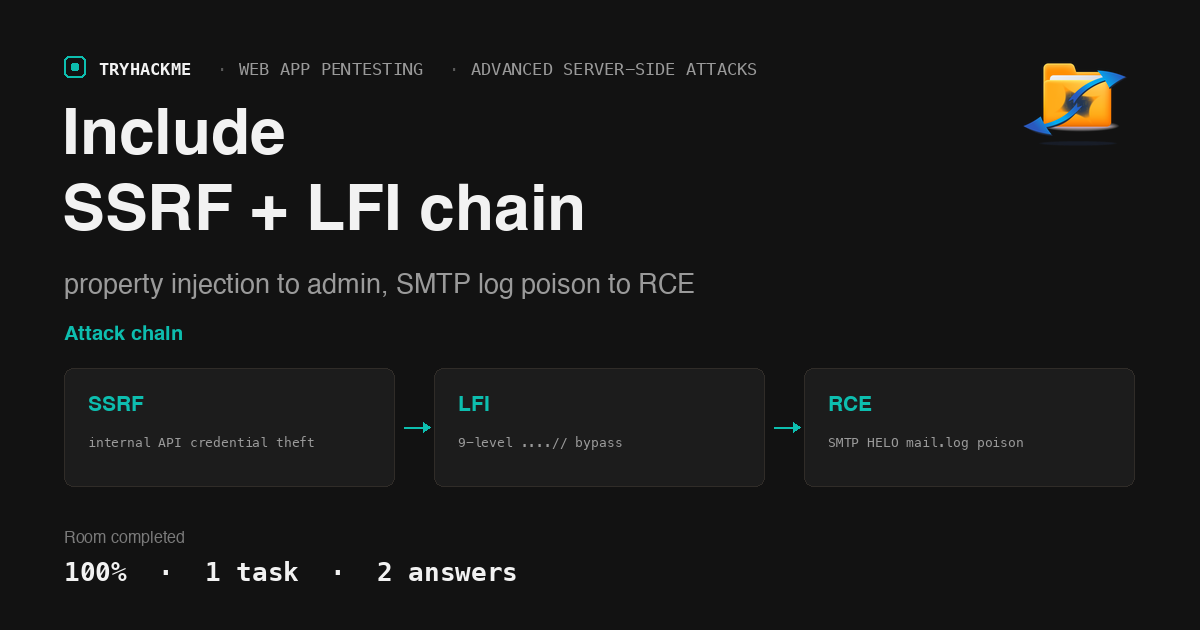
Include: from property injection to log poisoning RCE
prototype pollution
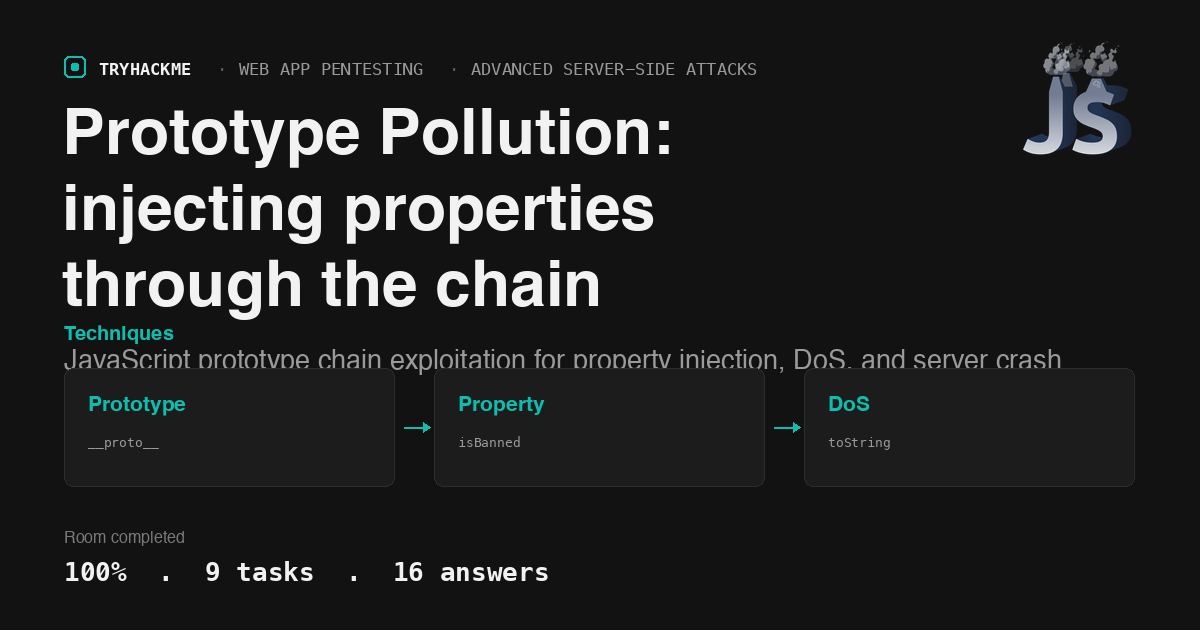
Prototype Pollution: injecting properties through the chain
file inclusion
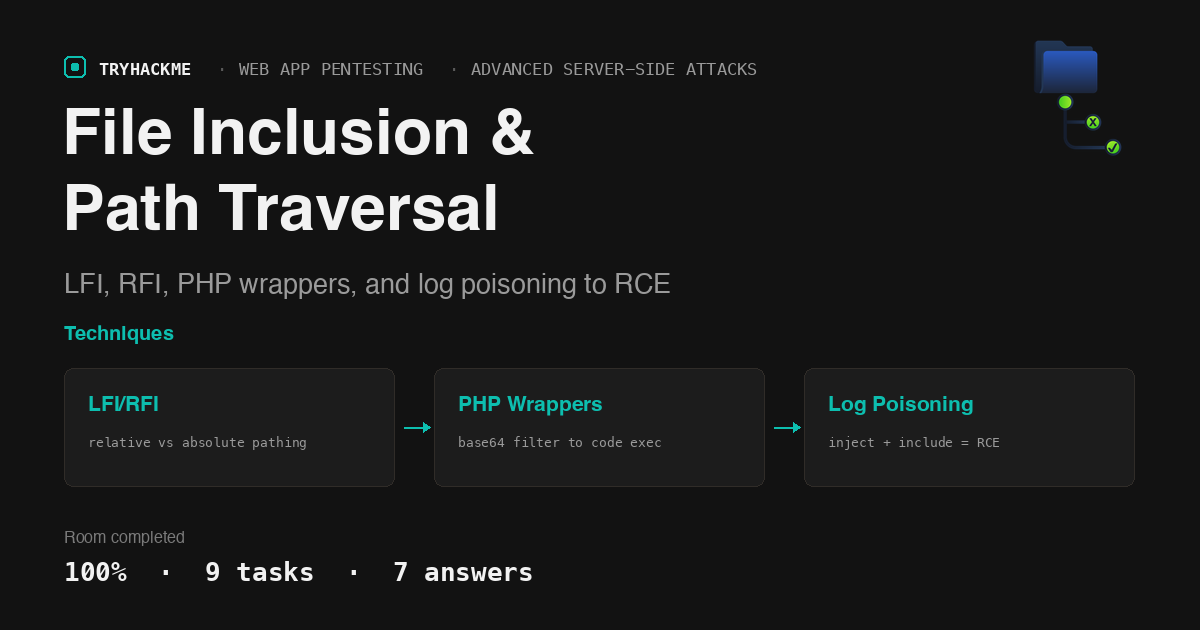
File Inclusion: from path traversal to code execution
SSRF
SSRF: forging requests from the server side
XSS
Whats Your Name: XSS, CSRF and SQLi chain