Dive Into Pentesting
The conceptual opener to the Penetration Testing Foundations module on the Jr Penetration Tester path, the same module as Guided Pentest: Web and Guided Pentest: Infrastructure. Those two are hands-on; this one is the theory that should sit under them. There is no lab machine and no exploitation, just eight tasks of reading and a single flag at the end.
A theory room is only worth writing up if it either clarifies something genuinely useful or has one technical wrinkle worth keeping. This one has both: the vocabulary that the rest of the path assumes you already know, and a final “activity” whose flag can be read directly rather than played. I have kept the answers grouped by concept and put the honest technical note at the end.
Task 2: Pentesting vs malicious hacking
The shortened term for penetration testing is pentesting. The room’s core table contrasts a tester with an attacker across authorisation, scope, and coverage. Two answers come straight out of it: the actor that aims for broad coverage and assesses multiple areas of a system is the Penetration Tester, and the one that focuses on the quickest path to success is the Attacker.
The distinction that actually matters here is not the tooling (which overlaps heavily) but authorisation and scope. A tester works from written consent inside agreed boundaries; an attacker is bound by neither. Everything else in the module descends from that one difference.
Task 3: Focus areas
Two answers about where testing effort goes. A network test performed from an external user perspective against internet-facing infrastructure is External network penetration testing (as opposed to the internal “assumed breach” variant). And session cookies that stay valid after logout fall under Session management, specifically the “session invalidation after logout” weakness, not authentication.
That second one is a common mislabel. Login handling is authentication; what happens to a session after login, including whether logout actually kills it, is session management. Getting the category right is what makes a finding land in the correct part of a report.
Task 4: Vulnerability, threat, and risk
The risk management cycle has four stages: identification, analysis, mitigation, monitoring. Patching a high-severity issue you reported is the Mitigation stage (applying security patches, strengthening controls).
The second answer is a nice reminder that risk is contextual, not intrinsic to the bug. The same SQL-injection flaw is a higher risk on an External-facing application than an internal one, because exposure changes likelihood even when the vulnerability is identical. A tester who reports severity without context is only doing half the job.
Task 5: Why vulnerabilities exist
One answer. An “Upload Resume” feature shipped without guardrails, allowing an unrestricted file upload, is a case of Human Assumptions: the developer assumed users would only upload the expected file type and never added validation. This is the same class of bug I exploited for real in Guided Pentest: Web, where an accept attribute filtered the file picker but the server trusted a blocklist. The theory here names the root cause that the practical room made you exploit.
Task 6: The pentester mindset
Three of the room’s named habits. Attacking a system without understanding how it works is Rushing to exploitation, the headline entry in the “ineffective mindset” column. The practice that makes findings reproducible later is Maintaining Good Notes (detailed notes let you revisit an early finding without repeating the whole process). And the habit that keeps blockers from eating your coverage is Proactive Communication: flagging roadblocks early so effort can be redirected before they cost you.
The through-line is that a pentest is a time-boxed engagement, so the mindset habits are really about spending a fixed budget well: understand first, document as you go, and surface problems early rather than burning hours in silence.
Task 7: Ethics, permission, and trust
Three one-word-ish answers. What defines the boundaries of a test is Scope. The kind of impact a finding should demonstrate is Business impact (not just technical severity). And the data that must be removed from reports to prevent unintended disclosure is Sensitive data, which the room frames as redaction.
These are the answers a grader wants, but the substance is worth internalising for the practical rooms: on both Guided Pentest boxes I redacted looted credentials in the evidence rather than reprinting them, which is exactly the “handle sensitive data responsibly” principle this task is testing.
Task 8: The flag, read rather than played
The final task sends you to a “View Site” activity: a short decision-making exercise that presents a flag on completion. You can play it, or you can notice that the activity is a static single-page app and the flag ships inside its JavaScript bundle.
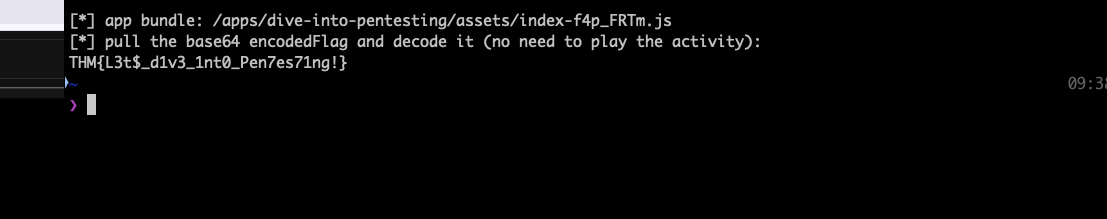
The app loads in an iframe from static-labs.tryhackme.cloud. Pulling the bundle and grepping for the base64-encoded flag skips the game entirely:
B=https://static-labs.tryhackme.cloud/apps/dive-into-pentesting
JS=$(curl -s "$B/" | grep -oE '/apps/[^"]+index-[^"]+\.js' | head -1)
curl -s "https://static-labs.tryhackme.cloud$JS" \
  | grep -oE '"VEhN[A-Za-z0-9+/=]+"' | tr -d '"' | base64 -d
  # THM{L3t$_d1v3_1nt0_Pen7es71ng!}
The flag is THM{L3t$_d1v3_1nt0_Pen7es71ng!}. The VEhN prefix is the tell: it is the base64 encoding of THM, so grepping for it finds the encoded flag directly among the minified strings. The bundle stores it as encodedFlag and decodes it client-side with atob(), which means the answer was never actually gated by completing the activity.
Two things worth keeping
The vocabulary is load-bearing, so learn it precisely. Session management versus authentication, mitigation versus the other risk stages, business impact versus technical severity: these are the exact distinctions a report is graded on, and the practical rooms assume you already draw them. A theory room is easy to skim, but the whole point of this one is the precision, an “authentication” finding that is really a session-management issue is a wrong label even when the bug is real.
A client-side flag is not a secret. The Task 8 activity presents its flag as a reward for making the right decisions, but the flag lives in the app’s JavaScript, base64-encoded and decoded in the browser. Anything a static site can show you, it has already shipped to you; the VEhN (THM in base64) grep is a general trick for these “View Site” activities. That is not cheating so much as understanding where the trust boundary actually is, which is the entire subject of the room.
Room solved 100%: 8 tasks, 15 answers.