Classroom
Paths
Posts
Tags
Search
About
Home
Tags
Blue Team
DFIR
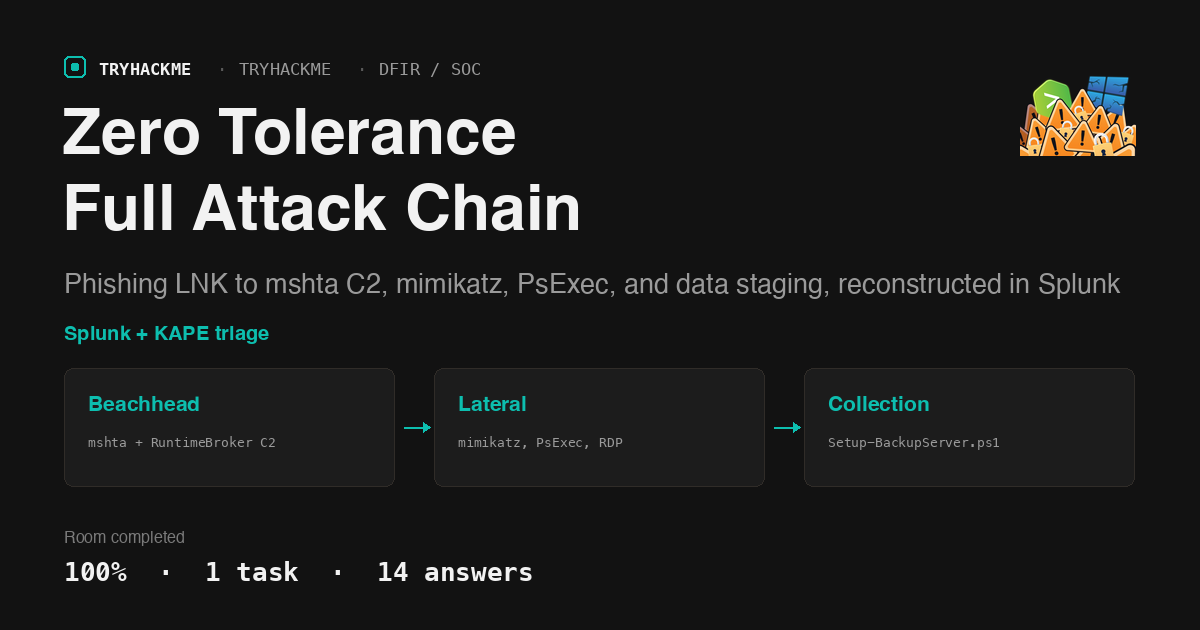
Zero Tolerance: Trace a Full Attack Chain in Splunk
DFIR
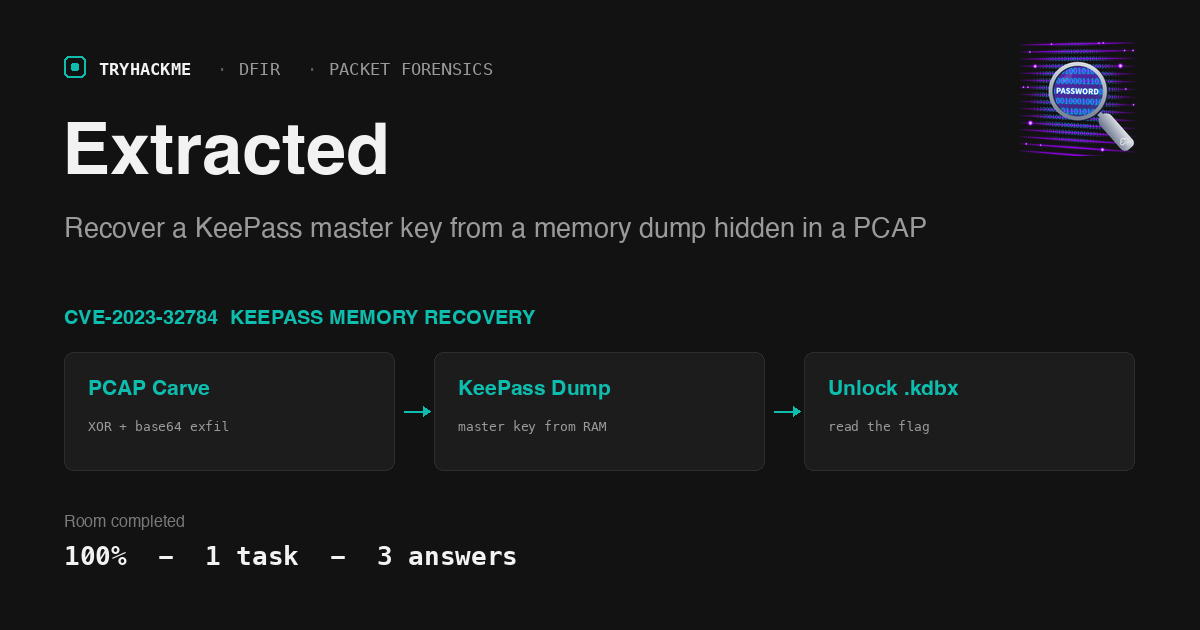
Extracted: Recover a KeePass Master Key from a PCAP
DFIR
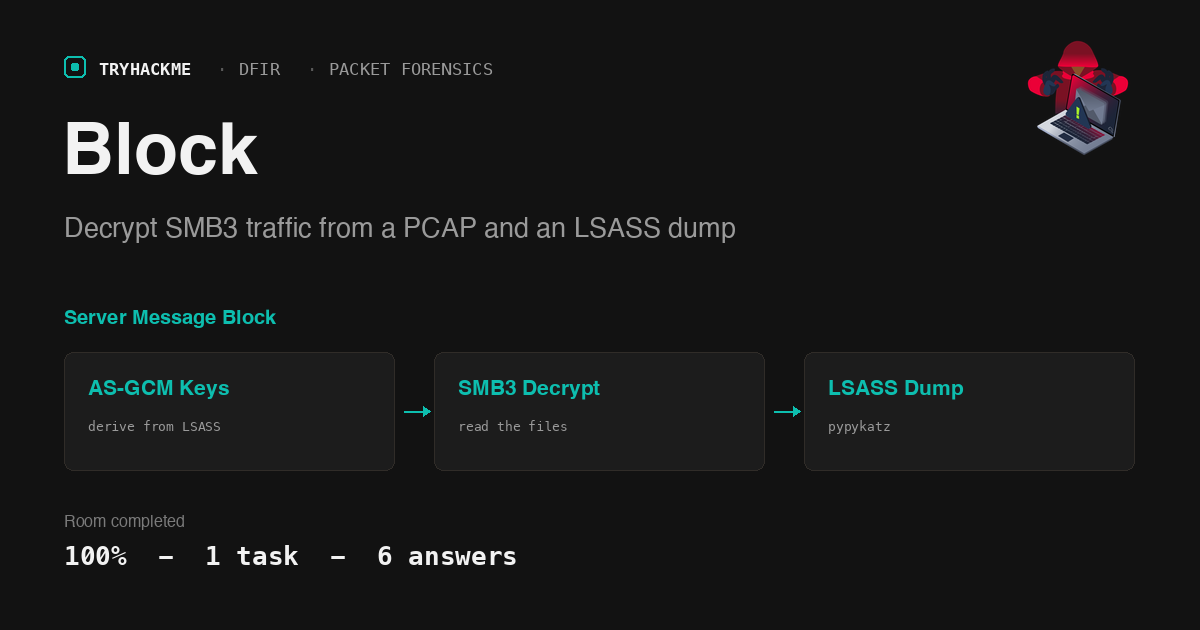
Block: Decrypt SMB3 Traffic from a PCAP and LSASS
DFIR
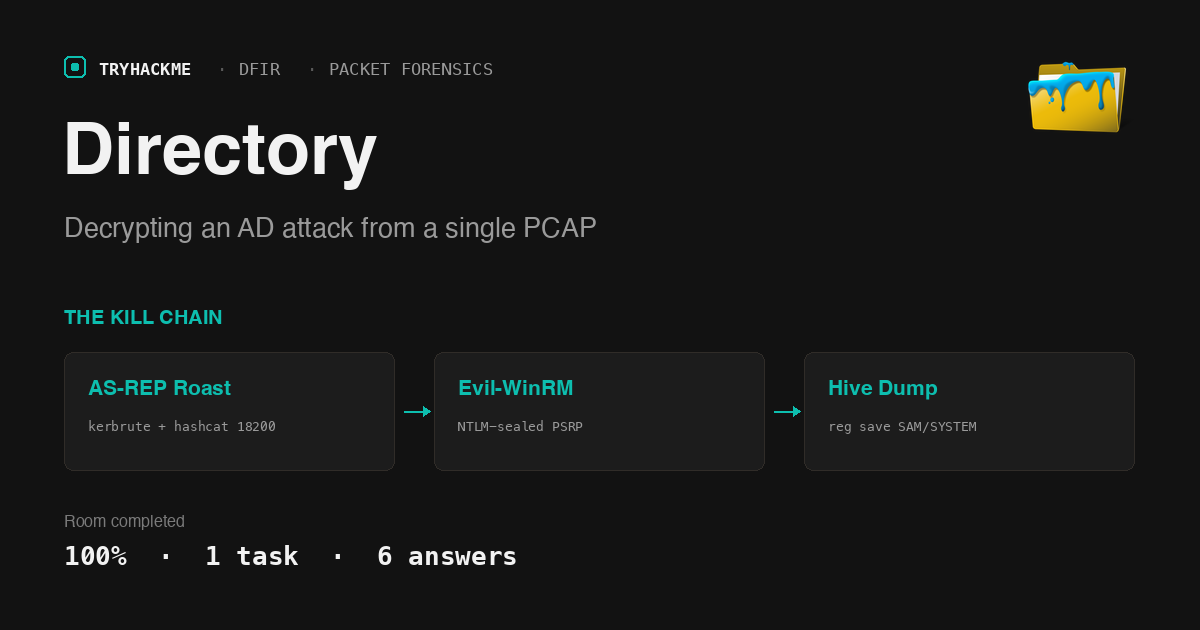
Directory: Decrypt an AD Attack from a PCAP
Zeek
Zeek Exercises: DNS Tunnel, Phishing and Log4Shell
Jr Penetration Tester
The Blue Team Perspective: Splunk BOTSv1 Triage
Jr Penetration Tester
Cyber Kill Chain: The Seven Phases Explained
Jr Penetration Tester
Dive Into Pentesting: Concepts, Ethics, Mindset
SOC Level 2
Conti: ProxyShell to Ransomware in Splunk
SOC Level 2
Monday Monitor: Reading Sysmon in Wazuh