Classroom
Paths
Posts
Tags
Search
About
Home
Tags
Web Application Red Teaming
Attacking LLMs
Juicy: XSS to SSRF via unsanitised LLM output
Attacking LLMs
Model Poisoning: supply chain and training data attacks
Attacking LLMs
LLM Output Handling: XSS and RCE via model output
Bypassing WAF
WAF Exploitation Techniques: encoding and evasion
Bypassing WAF
WAF Introduction: from packet filters to OWASP CRS rules
Bypassing WAF
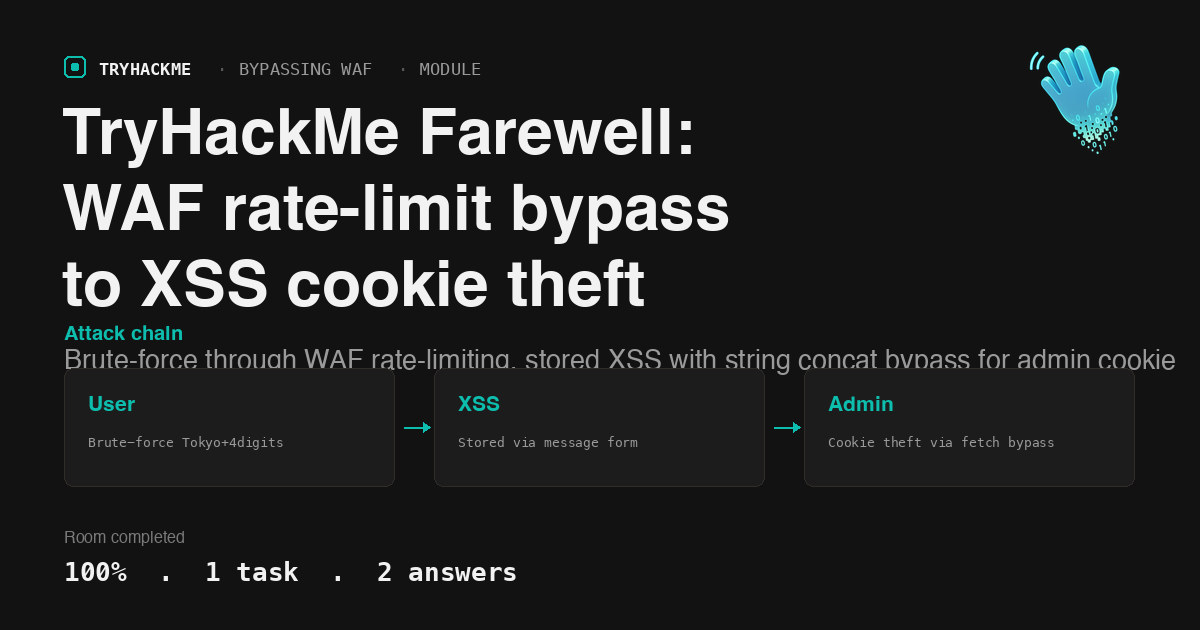
Farewell: WAF rate-limit bypass to XSS cookie theft
Bypassing WAF
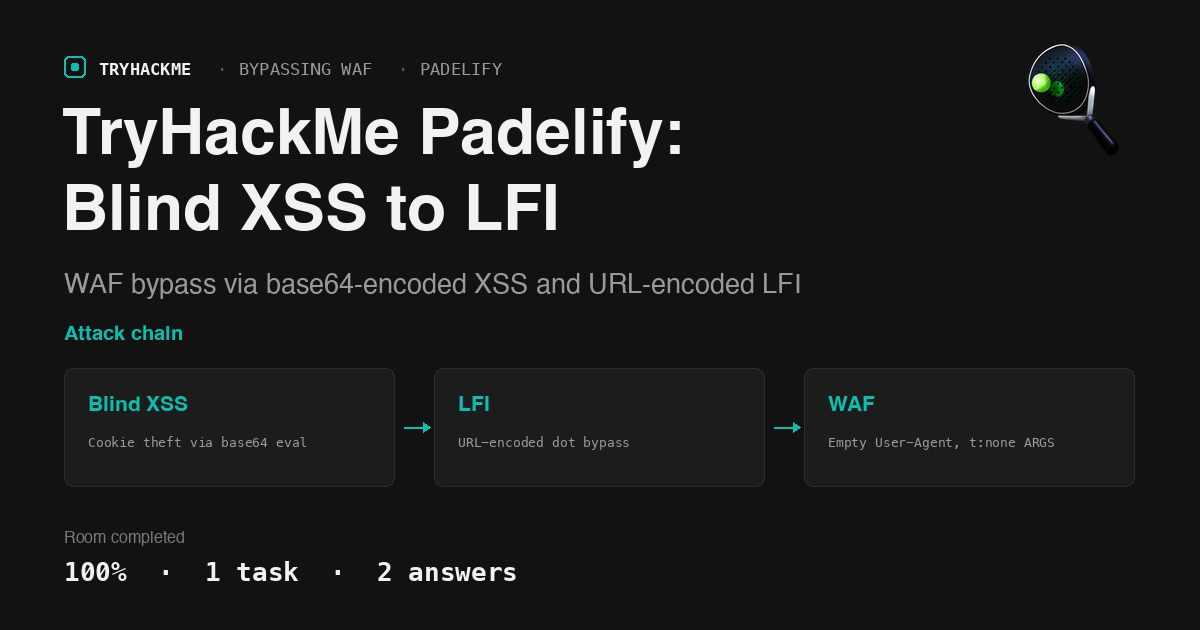
Padelify: blind XSS cookie theft to LFI admin takeover
stored XSS
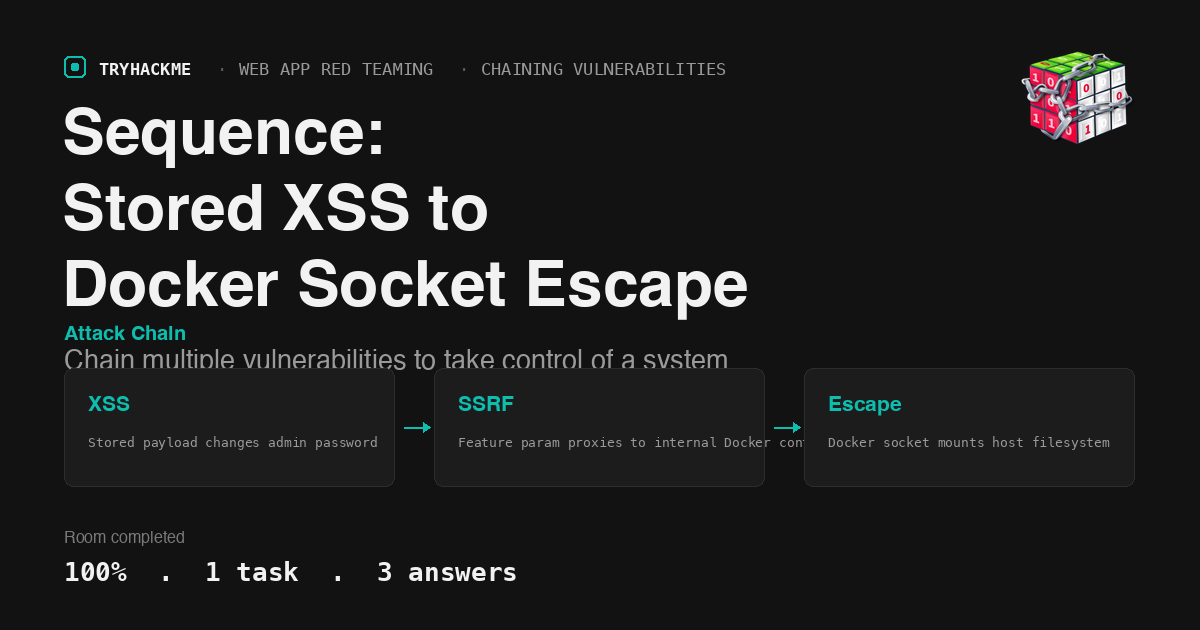
Sequence: stored XSS to Docker socket escape
container escape
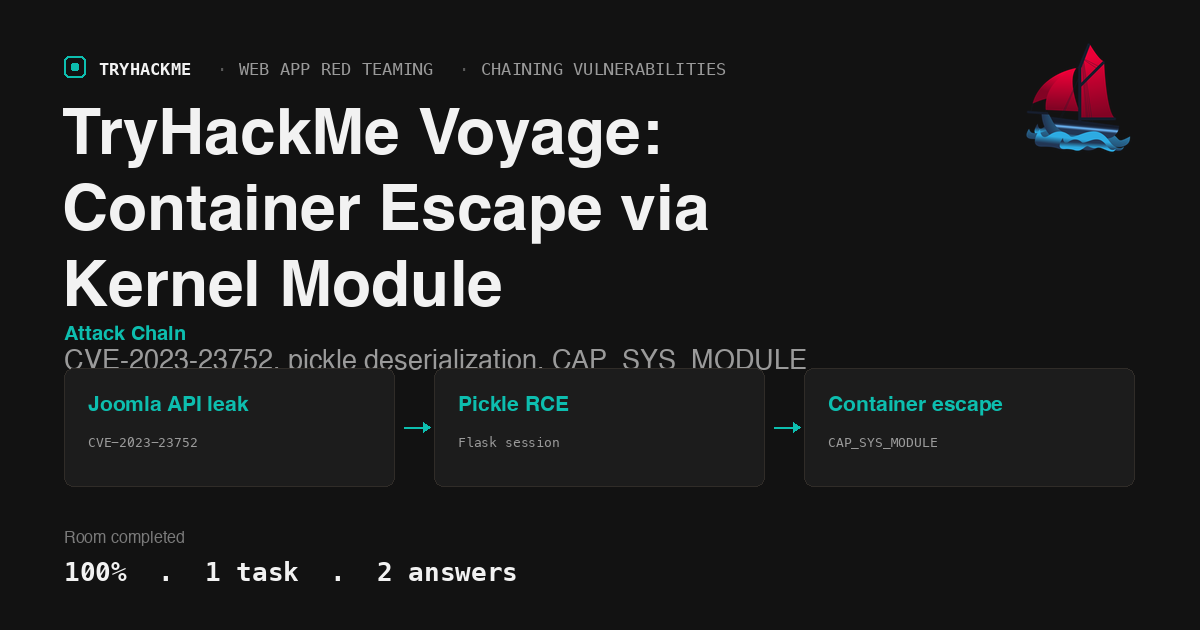
Voyage: container escape via kernel module
SSRF
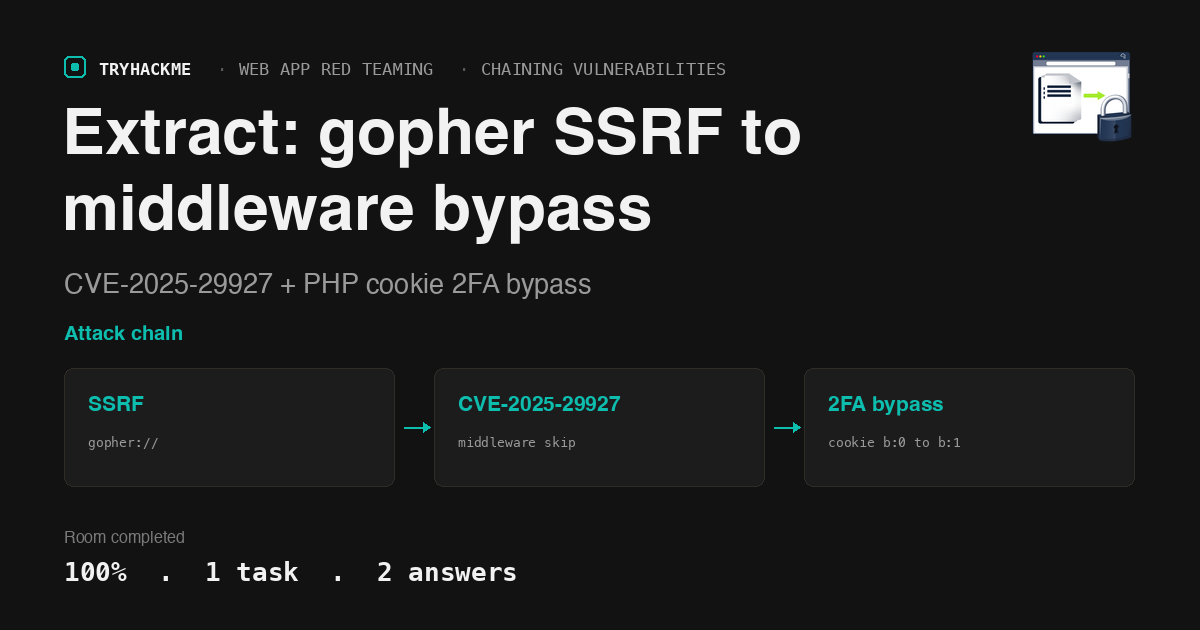
Extract: gopher SSRF to middleware bypass